A cyber incident can start with a device nobody remembers: a NAS left behind after an office move, a test PC set up for a pilot that never ended, or a smart gadget plugged in by facilities. If it has no owner, nobody updates it, nobody changes its passwords and nobody notices when it behaves oddly. The fix starts with finding it, and the firewall and switches you already own can usually show you what is connected.
Below is how such an incident typically unfolds, told generically, and how asset discovery works on the Fortinet FortiGate 50G and FortiGate 30G, the TP-Link Omada OC200 controller and ER7206 gateway, and HPE Networking Instant On switches such as the 1930.
How can a forgotten device turn into an incident?
| Stage | What typically happens | What would have caught it |
|---|---|---|
| 1. Forgotten | A device stays connected after its project, owner or office move | An asset inventory with a named owner per device |
| 2. Drift | Firmware falls behind; default or shared admin passwords never change | An update routine and a password review for every device |
| 3. Exposure | Remote access or a port-forwarding rule set up "temporarily" stays open | A periodic review of firewall rules, each tied to an owner |
| 4. Spread | On a flat network, the device can reach file shares and staff PCs | VLAN segmentation with firewall policy between segments |
| 5. Late discovery | Nobody watches the device, so problems surface only when data or systems are affected | Device detection, client lists and alerts on the network |
Why are forgotten devices such an easy way in?
Because the protections on managed laptops are missing. A forgotten device rarely runs endpoint protection, reports to nobody, and often keeps the credentials it shipped with. CISA has published a Secure by Design alert urging manufacturers to "proactively eliminate the risk of default password exploitation"; until every device arrives that way, changing credentials is your job.
The PDPA adds a business reason. The PDPC's Protection Obligation requires organisations to make "reasonable security arrangements" for the personal data in their possession, "to prevent unauthorised access, collection, use, disclosure or similar risks". A forgotten NAS of HR scans still counts. For common unmanaged devices and end-of-support dates, see The Most Dangerous Device in Your Office Might Be the One Nobody Manages; this post focuses on how to find them.
What does the path from forgotten device to incident look like?
Picture three ordinary devices. A test PC was set up in a meeting room for a software trial and left on the network. A two-bay NAS from the previous office still holds an old copy of the shared drive. A smart display in reception was installed by a contractor whose account still has admin access. None of them is malicious. Each is simply unwatched.
Over months, their software ages. If one has a remote-access rule left open on the firewall, or an outdated admin page, it becomes a weaker door than anything IT looks after. On a flat network, whoever gets through that door sits on the same segment as the finance PCs and the file server. Because nothing alerts on the forgotten device, the first sign may be an encrypted share or an unexpected data leak, and recovery becomes a continuity problem: see When Ransomware Strikes, Can Your Business Still Communicate?
SourceIT's take: the device you cannot name is the one you cannot defend. Make the network tell you what is plugged in.
Start with an inventory that has owners
CSA's Cyber Essentials mark is a useful yardstick for Singapore SMEs. In CSA's Cyber Essentials requirements for ICT vendors, the asset inventory must include third-party software and tools and "shall be reviewed at least once a year", with "mitigating stop-gap measures" where something cannot be fixed straight away. That suits any office: a yearly full review, plus a check whenever someone joins, leaves or moves.
Record each device's name, location, owner, purpose, firmware or OS version and a retirement date. Then use the network itself to find what the spreadsheet missed.
How do you find unknown devices on a FortiGate?
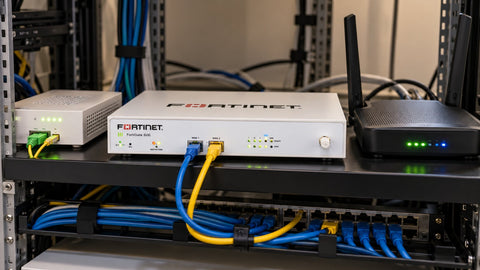
FortiOS, which runs on FortiGate models including the 30G and 50G, has a Device Detection feature. Fortinet's technical tip explains that enabling it lets FortiOS "monitor networks and gather information about devices operating on those networks", including MAC address, IP address, operating system, hostname, username, endpoint tags, and when and on which interface each device was detected. It is enabled per interface under Network > Interfaces on LAN, DMZ or undefined roles (not WAN), with care advised on busy guest Wi-Fi. Results appear under Dashboard > Users & Devices, renamed Assets and Identities from FortiOS 7.4.2.
In practice, enable detection on internal interfaces and compare the list with your inventory. Anything with an unfamiliar hostname or operating system goes on a follow-up list, and firewall policy between segments stops a forgotten box reaching everything else. Sizing advice is in Firewall Fit for Small Businesses.
How do Omada and Instant On show what is connected?
Controller-managed networks give you a client list for free. In Omada, the client list shows each device's name, IP address, MAC address, connection type and uptime, and can be filtered by device, network or SSID, with a separate view of blocked clients. The TP-Link Omada OC200 Hardware Controller (price on request) manages up to 100 Omada access points, 20 switches and 10 routers per its listing, and lists rogue AP detection, which flags unauthorised wireless transmitters such as a personal router someone added. The TP-Link Omada ER7206 Gigabit VPN Gateway (price on request) lists ARP scanning, IP-MAC binding and country-based access control at the edge.
HPE Networking Instant On does the same through its app and web portal. Its help centre describes a clients list covering wired, wireless and VPN clients, with MAC and IP address and the switch or access point and interface each one is connected to. Wireless clients can be blocked, any client can be put on a watchlist that raises an alert when it goes offline, and wired PoE clients can be power cycled on supported firmware. The HPE Networking Instant On 1930 24-Port Smart-Managed Switch (JL682A, S$408.00, in stock) adds VLANs, so a device you cannot retire yet can be fenced off. More tips are in best practices for managing Aruba Instant On networks.
What should you do when you find a forgotten device?
- Identify it. Find the owner and purpose. If nobody claims it, disconnect it and see who asks.
- Check what it holds. Personal data or old shared drives raise the priority.
- Update, isolate or retire. Patch it and change every credential, move it to its own VLAN, or wipe and dispose of it properly.
- Close the doors it used. Remove stale firewall rules and remote-access accounts tied to it.
- Add it to the inventory with a review date.
Meeting rooms and AV kit are frequent hiding places; see Your Video Conference Is Confidential. But What About the Room Equipment?, Another Cyberattack in the Headlines. But Is Your Meeting Room Secure? and The Next Cybersecurity Incident Could Come Through Your Video Wall. Printers are covered in Your Office Printer Could Be the Weakest Link in Your Network.
Buying firewalls and managed networking in Singapore
SourceIT supplies Fortinet, TP-Link Omada and HPE Networking Instant On with local warranty; the Omada listings state 5 years of local warranty, and for other items confirm the term for your SKU when requesting a quote. As listed on 24 Oct 2026, the Fortinet FortiGate 50G (FG-50G, five GE RJ45 ports) is S$1,168.80 for hardware only or S$1,819.20 with 1-Year Unified Threat Protection, and the Fortinet FortiGate 30G (FG-30G, four GE RJ45 ports) is S$766.80 for hardware only or S$1,236.00 with 1-Year UTP; both were in stock. Browse Fortinet FortiGate firewalls or TP-Link Omada business networking. Use Request for Quotation on the product page, call (65) 6978 3502, email Sales@sourceit.com.sg or use our contact page. We are GeBIZ / Vendors@Gov registered for government buyers.
Frequently asked questions
How do I find all devices on my office network? Combine a physical walk-round with your network's own lists: device detection on the firewall, client lists in your switch or Wi-Fi controller, and DHCP leases. Compare the results with your asset inventory and follow up anything unknown.
Can a FortiGate identify devices on my network? Yes. Fortinet's Device Detection, enabled per internal interface, records MAC address, IP address, operating system, hostname and when and where each device was seen. Results appear under Assets and Identities in FortiOS 7.4.2 and later.
Does Omada show connected clients? Yes. The Omada client list shows device name, IP and MAC address, connection type and uptime, and can be filtered by device, network or SSID. Controllers such as the OC200 also list rogue AP detection.
Can Instant On alert me about a device? Instant On lets you add a client to a watchlist, which raises an alert when that client goes offline. Wireless clients can also be blocked from the site.
How often should we review our IT asset inventory? CSA's Cyber Essentials requirements for ICT vendors ask for a review at least once a year. Many offices also check whenever staff join, leave or move.
What should I do with a device nobody owns? Disconnect or isolate it, check what data it holds, then update it and change its credentials or wipe and retire it. Remove any firewall rules or accounts created for it.

SourceIT Approved
Researched and verified by the SourceIT team for Singapore buyers.