The Most Dangerous Device in Your Office Might Be the One Nobody Manages

The most dangerous device in your office is usually not the newest laptop or the firewall. It is the old NAS in the storeroom, the unmanaged switch under a desk, the smart plug someone brought in, or the server nobody has logged into for two years. If no one owns it, no one patches it, and anything on the same flat network as your staff laptops is only as safe as that forgotten box.
This post makes the case for an owner for every device, explains how to find the unmanaged ones, and shows the network controls that contain them, using the Fortinet FortiGate-60F, FortiGate-40F and HPE Networking Instant On 1930 and 1830 switches as examples.
Which unmanaged devices are hiding in a typical office?
| Device | Why it gets forgotten | Risk | First fix |
|---|---|---|---|
| Old NAS or file server | Still "works", nobody wants to touch it | Unpatched firmware, shared admin passwords, company data inside | Assign an owner, update or retire, check backups |
| Server on end-of-support Windows | Runs one legacy app | No more security updates from Microsoft | Plan migration; isolate it until then |
| Unmanaged or consumer switch | Added to get "one more port" | No VLANs, no visibility, loops | Replace with a managed switch |
| Personal router or Wi-Fi extender | Staff wanted better signal | Unknown wireless network bridging into the LAN | Remove; fix coverage properly |
| Smart plugs, sensors, TVs, printers | Bought by facilities, not IT | Default passwords, cloud apps, rare updates | Separate IoT VLAN, change defaults |
| Former staff or contractor kit | Never collected | Saved credentials and VPN profiles | Offboarding checklist |
Why is an unmanaged device more dangerous than a managed one?
A managed device has an owner, a patch routine and a place in an inventory. An unmanaged one has none, so it drifts. Windows is the clearest example. Microsoft states that Windows 10 reached end of support on 14 October 2025, and that a PC still running it "will no longer receive regular security updates". Extended Security Updates exist, but Microsoft describes them as "critical and important security updates only", with no feature updates or general technical support. A Windows 10 PC that IT does not know about is not enrolled in anything.
Servers follow the same pattern. Microsoft's lifecycle page for Windows Server 2012 R2 shows extended support ended on 10 October 2023, and the last paid Extended Security Updates year it lists ran out in October 2026. Windows Server 2016's extended support ends on 12 January 2027, less than three months from today. If a 2016 box is quietly running accounts or a door-access system in your comms cupboard, now is the time to plan. Our earlier post on preparing for the end of Windows Server 2012 walks through the migration choices.
Under the PDPA, this is not only an IT tidiness issue. The PDPC's Protection Obligation requires organisations to make "reasonable security arrangements" to protect personal data in their possession "to prevent unauthorised access, collection, use, disclosure or similar risks". An unpatched NAS full of HR files is hard to describe as reasonable.
The case for leaving things alone
There is a fair counter-argument. Small offices run on goodwill and limited time. The old NAS works, the legacy app vendor has closed, and replacing the server means downtime nobody budgeted for. Locking everything down can also push staff towards workarounds, which is how personal routers appeared in the first place. And a device that is offline, or holds nothing sensitive, may be a low priority.
We agree with part of this. Not every forgotten device needs replacing this month. But "leave it alone" only works if you know it exists, know what it holds and have fenced it off. The danger is not old hardware; it is old hardware nobody has thought about.
SourceIT's take: you cannot secure what you have not counted. Inventory first, segment second, replace third.
How do you find every device on your office network?
Start with a list. CSA's Cyber Essentials mark groups its measures under Assets (people, hardware and software, data), Secure/Protect, Update, Backup and Respond, and the inventory comes first for good reason. CSA's Cyber Essentials document for ICT vendors also asks for the asset inventory to be reviewed at least once a year. A practical routine for an SME:
- Walk the office. Check comms cupboards, under desks, meeting rooms and the storeroom. Photograph labels and serial numbers.
- Read the firewall and switch tables. DHCP leases on the firewall and MAC address tables on managed switches show what is actually connected. An unmanaged switch hides this.
- Give each device an owner, a purpose and an end date. If nobody claims it, disconnect it and see who complains.
- Record operating system and firmware versions, then check them against vendor lifecycle pages.
- Prefer certified smart devices. Under CSA's Cybersecurity Labelling Scheme for IoT, even Level 1 means the product meets basic requirements "such as ensuring unique default passwords and providing software updates".
Printers and displays deserve their own review: see Your Office Printer Could Be the Weakest Link in Your Network and Your Smart TV Might Know More About Your Office Than You Think. Meeting room cameras are covered in Are Smart Meeting Room Cameras a Privacy Nightmare?
How do you contain devices you cannot replace yet?
Segmentation is the safety net. Put staff laptops, servers, guest Wi-Fi, IoT and AV equipment on separate VLANs, and let the firewall decide what may talk to what. A legacy server then only accepts traffic from the PCs that use its app, and a smart plug cannot reach the file server at all. The same approach answers the BYOD question in Should Companies Ban Personal Laptops From Their Office Network?
For the switches, the HPE Networking Instant On 1930 24-Port Gigabit Smart-Managed Switch (JL682A, S$408.00, in stock) lists VLANs, IEEE 802.1X access control with RADIUS, ACLs and four 10G SFP+ uplinks, and is fanless. For a meeting room or reception desk where someone would otherwise add a consumer switch, the HPE Networking Instant On 1830 8-Port Smart-Managed Switch (JL810A, S$201.60, in stock) brings VLANs and access control to eight ports. Both are managed from the Instant On app, cloud portal or local web GUI, and the listings state no extra licence or subscription fee. Our post on managing Aruba Instant On networks has setup tips.
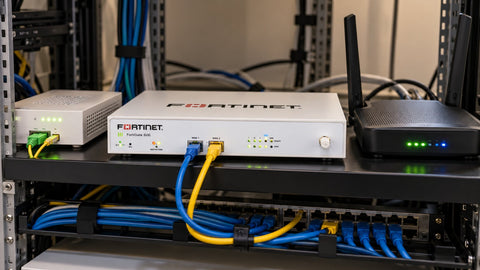
At the edge, the Fortinet FortiGate-60F with 24x7 FortiCare and UTM Protection (FG-60F-BDL-950-12, S$1,535.00 for the 1-year bundle, available to order) bundles antivirus, intrusion prevention, web filtering and application control, and routes between VLANs under firewall policy. Smaller offices can look at the Fortinet FortiGate-40F UTM bundle (FG-40F-BDL-950-12, S$1,065.00 for 1 year, available to order). For sizing, read Firewall Fit for Small Businesses, and for the bigger picture, our ransomware prevention guide.
Verdict: who should own the forgotten box?
Someone, by name. The fix for unmanaged devices is mostly process: an inventory reviewed regularly, an owner for every box, and a retirement date for anything past vendor support. Hardware helps by making the network visible and fenced. Leavers' kit belongs in the same loop; Your Ex-Employee Might Still Have Access to Company Data has the checklist.
Buying firewalls and managed switches in Singapore
SourceIT supplies Fortinet and HPE Networking Instant On with local warranty; the Instant On listings state HPE's Limited Lifetime warranty. Prices are as listed on 23 Oct 2026. Browse Fortinet FortiGate firewalls or HPE Networking Instant On. Use Request for Quotation on the product page, call (65) 6978 3502, email Sales@sourceit.com.sg or use our contact page. We are GeBIZ / Vendors@Gov registered for government buyers.
Frequently asked questions
What is an unmanaged device? Any device on your network without a named owner, an update routine and an inventory record: old NAS boxes, consumer switches, personal routers, smart plugs and forgotten servers are common examples.
Is it safe to keep using Windows 10 in the office? Microsoft ended Windows 10 support on 14 October 2025, and PCs no longer receive regular security updates. Extended Security Updates cover critical and important security fixes only. Plan upgrades and isolate any PC that must stay.
When does Windows Server 2016 reach end of support? Microsoft's lifecycle page lists the extended end date as 12 January 2027 (Pacific Time). Plan migration or isolation before then.
How do I separate IoT devices from staff computers? Use a managed switch with VLANs and a firewall that controls traffic between VLANs, so smart devices can reach the internet but not your file servers.
Does the PDPA cover forgotten devices? The PDPA's Protection Obligation requires reasonable security arrangements for personal data in your possession, wherever it sits, including an old NAS or server.
What does the Cybersecurity Labelling Scheme tell me? CSA's CLS for IoT rates smart devices from Level 1 to 4. Level 1 means basic requirements such as unique default passwords and software updates are met.