When ransomware strikes, your business can still communicate only if you planned how before it happened. The first response to an infection is usually to disconnect affected systems, which can take email, file shares, office phones and the incident plan itself offline at the moment you need them. A short written plan, an offline contact list, a separate way to talk and backups the attacker cannot reach are what keep the business talking.
This guide covers out-of-band communication, who to notify in Singapore, the backup rules that survive an attack, and the kit that supports them, including the Synology DiskStation DS925+ and DS225+, Fortinet FortiGate 50G, APC Back-UPS Pro BR900MI and TP-Link Archer MR505 4G router.
What can ransomware take down, and what is the fallback?
| What you rely on | Why it may be unavailable | Fallback to prepare now |
|---|---|---|
| Email and chat on company laptops | Laptops isolated; accounts may be under the attacker's watch | Agreed out-of-band channel on separate devices, such as phone calls |
| Contacts in Outlook or the CRM | Systems offline or untrusted | Printed and offline contact list, updated quarterly |
| Incident plan on the file server | Encrypted with everything else | Hard copy plus an offline copy |
| Shared drives and NAS | Encrypted or disconnected for containment | Offline or immutable backups, tested |
| IP desk phones on the office LAN | Network segments shut down | Mobile numbers and call forwarding |
| Office internet | Main network disconnected while investigated | Separate connection for clean devices only |
Why does communication break first in a ransomware incident?
Because containment works against convenience. The Singapore Police Force's ransomware advice is to "disconnect the infected computer from all network access, storage devices and Bluetooth devices". Done properly across an office, that can cut off the tools people normally use to coordinate. There is a second problem: if an attacker has access to email or chat, using those channels to plan the response may tell them what you are doing. The #StopRansomware Guide published by CISA, MS-ISAC, NSA and FBI advises responders to "use out-of-band communication methods such as phone calls to avoid tipping off actors".
So the question is not which app to use. It is which channel stays separate from the systems under investigation, and who has the numbers.
What should an out-of-band communications plan include?
- A named decision-maker and a deputy, with personal mobile numbers.
- A contact sheet. The #StopRansomware Guide includes a response-contacts table; fill in your own with IT support, your firewall and backup providers, insurer, legal adviser, key suppliers and major customers.
- A hard copy. CISA's guide says to "ensure a hard copy of the plan and an offline version is available".
- A decision log. The international Counter Ransomware Initiative guidance, which Singapore and the UK led according to CSA, recommends a careful record of decisions and actions kept offline or on systems the incident has not affected.
- Holding statements for staff, customers and suppliers, drafted in advance and approved by management.
- A clean device rule: only devices known to be unaffected join the response.
The CRI guidance also asks organisations to treat this as "preparation, as part of their business continuity plan", with communications plans ready in advance. For the wider continuity picture, see The Haze Might Be Temporary. Your Business Continuity Problems Aren't. and the practical Plan B checklist.
Who should you notify in Singapore?
SPF advises victims to lodge an online police report, and states that doing so also notifies SingCERT under the Cyber Security Agency of Singapore. If personal data is involved, the PDPC's Data Breach Notification Obligation requires you to assess whether the breach is notifiable and, if it is likely to result in significant harm to individuals or is of significant scale, notify the PDPC and affected individuals "as soon as practicable". The CSA and SPF Ransomware Portal collects advisories, reporting advice and incident response checklists.
On payment, both SPF and the CRI guidance strongly discourage it. SPF notes there is "no guarantee that paying the ransom will result in the decryption of your files", and the CRI guidance warns that payment "does not guarantee access to your devices or data". Get expert and legal advice early. Prevention measures are covered in our ransomware prevention guide.
Which backups survive a ransomware attack?
The ones the attacker cannot reach. SPF's advice is to back up "regularly in a separate system and keep it offline", and CISA's guide says to "maintain offline, encrypted backups of critical data" and regularly test them. A US EPA cybersecurity checklist frames this as the NIST 3-2-1 rule: three copies of data, on two different media types, with one copy offsite, and it recommends isolating backups from network connections and testing recovery of individual files.
A NAS is a good first backup target, but a NAS that is always mapped as a drive is not offline. Synology describes immutable snapshots in its Snapshot Replication feature as "a WORM technology" with mandatory protection periods, aimed at defending against ransomware and unwanted deletion, and snapshots can be replicated to another Synology system; confirm support for your model and DSM version when requesting a quote. The Synology DiskStation DS925+ (S$1,260.00, in stock) is a 4-bay NAS, expandable to 9 drives, which its listing suggests for Active Backup for Business and SME file services. The Synology DiskStation DS225+ (S$511.20, in stock) suits a small office or a second replication target in another location. Both listings state a 3-year Synology warranty and are diskless. For the offline copy, rotated media or tape still has a place; see LTO-7 vs LTO-8 vs LTO-9 and Your Expensive SSD Could Lose Data Without Warning.
SourceIT's take: a backup you cannot restore and a contact list you cannot open are the same thing. Print the list, test the restore.
What keeps the core of the network usable during recovery?
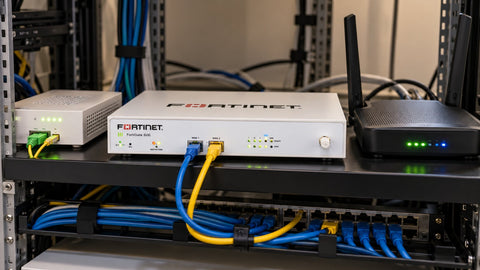
Recovery needs a trustworthy edge. The Fortinet FortiGate 50G (FG-50G) is S$1,168.80 for hardware only or S$1,819.20 with 1-Year Unified Threat Protection, which its listing says covers IPS, Advanced Malware Protection, application control, URL, DNS and video filtering, and FortiCare Premium support. Firewall policy between segments lets you bring clean systems back one at a time. How forgotten devices widen an incident is covered in A Cyber Incident Can Start With a Forgotten Device in Your Office.
A separate internet path helps clean devices reach the outside world while the main network is held for investigation. The TP-Link Archer MR505 4G+ Cat6 router (S$120.00, in stock) takes a nano SIM, which is not supplied, and lists WAN failover; keep it off the production network so it stays clean. Wider outage design is in Why the Next Major Internet Outage Should Change How You Design Your Office.
Power matters too: a NAS that loses power mid-restore costs time. The APC Back-UPS Pro BR900MI (S$452.50, in stock) is a 900 VA / 540 W line-interactive UPS with six battery-backed outlets, enough for a NAS, firewall and switch at modest loads. Size it with our UPS size calculator guide.
How do you know the plan works?
Rehearse it. CISA's guide says to "create, maintain, and regularly exercise" the response plan and its communications plan. A one-hour tabletop session is enough to start: assume email and file shares are gone, hand out the printed contact sheet, and see who can reach whom. Then restore one folder from the offline backup and time it. Meeting room systems, AV kit and USB policies belong in the same review; see Another Cyberattack in the Headlines. But Is Your Meeting Room Secure?, Your Video Conference Is Confidential. But What About the Room Equipment? and Would You Plug an Unknown USB Drive Into Your Office PC?
Buying backup, firewall and power equipment in Singapore
SourceIT supplies Synology, Fortinet, APC and TP-Link with local warranty; the APC BR900MI listing states a 2-year manufacturer warranty and the Archer MR505 listing 3 years, and for other items confirm the term for your SKU when requesting a quote. Prices are as listed on 24 Oct 2026, and all items above were in stock at the time of writing. Browse Synology backup and data protection or Fortinet FortiGate firewalls. Use Request for Quotation on the product page, call (65) 6978 3502, email Sales@sourceit.com.sg or use our contact page. We are GeBIZ / Vendors@Gov registered for government buyers.
Frequently asked questions
What is out-of-band communication in a ransomware incident? A way to coordinate that does not rely on the systems under investigation, such as phone calls on separate devices. CISA's #StopRansomware Guide recommends it to avoid tipping off attackers.
Where should we keep our incident response plan? In more than one place, including a hard copy and an offline version, as CISA's guide advises. A plan stored only on the file server may be encrypted with everything else.
How do I report ransomware in Singapore? SPF advises lodging an online police report, which also notifies SingCERT. If personal data is affected, assess whether the breach is notifiable to the PDPC.
Should we pay the ransom? SPF and the Counter Ransomware Initiative guidance strongly discourage payment, and SPF notes there is no guarantee of decryption. Seek expert and legal advice.
Is a NAS enough as a ransomware backup? Not on its own if it stays connected. Follow the 3-2-1 rule with one copy offline or immutable and one offsite, and test restores regularly.
What is the 3-2-1 backup rule? Three copies of your data, on two different media types, with one copy stored offsite. A US EPA checklist cites it as the NIST 3-2-1 rule.

SourceIT Approved
Researched and verified by the SourceIT team for Singapore buyers.