Should Companies Ban Personal Laptops From Their Office Network?

No, most companies should not simply ban personal laptops from the office. They should keep personal devices off the network segment where company data lives, give them internet-only guest access, and let them reach work apps only through controls such as app protection policies, compliant-device checks or a virtual desktop. A ban that people work around is less safe than a segmented network that people actually use.
This post weighs both sides of the BYOD (bring your own device) debate for Singapore businesses, sets out what the PDPA expects, and shows the kit that makes "segment, don't just ban" practical: a Fortinet FortiGate 50G firewall, HPE Networking Instant On AP22 access points, Microsoft 365 Business Premium and company-issued laptops such as the ASUS ExpertBook P3.
What are the options for personal laptops at work?
| Approach | Risk to company data | Friction for staff | Best for |
|---|---|---|---|
| Outright ban, no enforcement | Hidden: devices still connect via shared passwords or hotspots | High, so people work around it | Nobody, on its own |
| Guest Wi-Fi only, isolated from the LAN | Low on the network; data can still reach the device via cloud apps | Low | Visitors, personal browsing |
| Guest network plus app protection policies | Low to medium; company data stays inside managed apps | Low to medium | Email, Teams and files on personal devices |
| Compliant-device rule (Conditional Access) | Low; unmanaged devices cannot open protected apps | Medium | Sensitive data, regulated teams |
| Virtual desktop (Cloud PC) | Low; data stays in the cloud desktop | Medium | Contractors, occasional remote access |
| Company-issued laptop | Lowest; fully managed device | Low once issued | Staff who handle personal or financial data daily |
The case for banning personal laptops
The argument for a ban is simple: you cannot vouch for a device you do not manage. A personal laptop may run an out-of-date operating system, share a login with family members, carry pirated software or have no disk encryption. Plug it into the same network as the file server, the accounting PC and the printers, and its problems become yours. We make the wider point about unmanaged kit in The Most Dangerous Device in Your Office Might Be the One Nobody Manages.
The PDPA adds weight. The PDPC describes the Protection Obligation as making "reasonable security arrangements" to protect personal data in your organisation's possession, and its Data Breach Notification Obligation requires you to notify the PDPC and affected individuals where a breach is likely to cause significant harm or is of significant scale. Customer data sitting on an unmanaged personal laptop is hard to defend under either.
The case against a blanket ban
Bans are blunt. Staff in hybrid roles want to check email on their own laptop at home, contractors arrive with their own machines, and a small business may not be able to issue a laptop to every part-timer. A ban that blocks the Wi-Fi password simply pushes people to mobile hotspots and personal cloud storage, where you have even less visibility. The PDPC itself does not assume BYOD will disappear: its Guide to Securing Personal Data in Electronic Medium says protections for portable devices should apply whether they are issued by the organisation or "owned by employees (e.g. Bring Your Own Device or BYOD)". The same guide recommends remote locking and wiping for lost or stolen devices, and designing internal networks as zones "segregating the internal network according to function, physical location, access type etc."
Do not ask whether a personal laptop is allowed in the office. Ask what it can reach once it is there.
How do you segment the network for BYOD?
Start with Wi-Fi. Run at least two networks: an employee network for company-managed devices and a guest network that only reaches the internet. HPE Networking Instant On, for example, lets you set up separate networks for employee and guest users from its app. The HPE Networking Instant On AP22 Wi-Fi 6 access point is S$240.00 as listed on 23 Oct 2026, with WPA3 support and HPE's 2-year warranty; our guide to Aruba Instant On guest Wi-Fi walks through the setup.
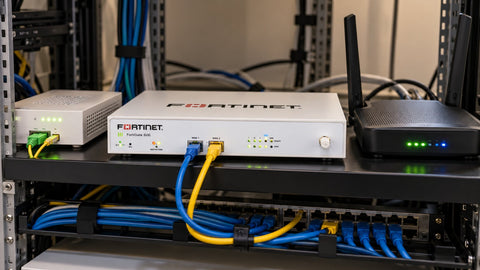
Then put a firewall between the zones. A next-generation firewall applies rules between the guest network, the staff network and the server or printer segment, so a personal laptop on guest Wi-Fi cannot browse to the file server. The Fortinet FortiGate 50G, S$1,168.80 as listed for the hardware-only option, is rated by Fortinet at 5 Gbps firewall throughput and 1.1 Gbps threat protection, and can be bundled with FortiGuard Unified Threat Protection. Our post on FortiGate firewalls for small businesses covers sizing. Larger sites may add network access control (NAC), which checks a device before it is admitted to a segment, but most SMEs get the bulk of the benefit from guest isolation and firewall rules.
How do you protect company data on a personal device?
Network segmentation stops a personal laptop reaching your servers, but cloud apps such as Outlook, Teams and OneDrive are reachable from anywhere. That is where identity and app controls come in. Microsoft says Intune app protection policies can be used "independent of any mobile-device management (MDM) solution", including on devices not enrolled at all, and apply "only in a work context". They can stop users copying company data into personal apps, control where copies are saved, require a PIN, and selectively wipe company data from an app without touching personal data.
For stricter teams, a Conditional Access policy can require a device "to be marked as compliant" before it opens protected apps, which effectively shuts out unmanaged laptops; Microsoft advises starting such a policy in report-only mode. For contractors, a virtual desktop is often the cleanest answer: Windows 365 Cloud PCs can be reached from a browser or app on Windows, Mac, iOS and Android, so the data stays in the cloud desktop rather than on the personal machine.
Licensing matters here. Microsoft's plan comparison lists Intune Plan 1, Microsoft Entra ID and Defender for Business as included in Microsoft 365 Business Premium, but not in Business Basic or Business Standard. The Microsoft 365 Business Premium annual subscription is S$335.00 per user as listed on 23 Oct 2026. Keeping those seats under control is its own job, covered in Your Company Has 20 Different IT Subscriptions. Who's Actually Tracking Them?
When should you issue company laptops instead?
If a role handles personal data, payroll or client files every day, a company-owned, managed laptop is simpler than policing a personal one. You control encryption, patching and remote wipe, and you get the device back when the person leaves (see Your Ex-Employee Might Still Have Access to Company Data). The ASUS ExpertBook P3 P3406CCA-LY0040X, S$2,099.00 as listed, ships with Windows 11 Pro ready for Entra ID join and Intune enrolment, a fingerprint sensor and IR camera for Windows Hello, and 3 years of ASUS onsite warranty. If cash flow is the obstacle, compare buying with Device-as-a-Service, and choose models you can keep running, as argued in Why Repairability Should Matter More Than Fancy Specifications.
SourceIT's verdict: segment, don't just ban
A blanket ban looks decisive but tends to fail quietly. Our recommendation for most Singapore SMEs is: personal laptops get guest Wi-Fi with internet-only access; company apps on personal devices sit behind app protection policies and multifactor sign-in; sensitive systems require a compliant, company-managed device; and roles that handle personal data daily get a company laptop. Write it down as a one-page BYOD policy so staff know the rules. For remote access, see secure remote access with Aruba Instant On.
Getting BYOD-ready in Singapore
SourceIT supplies Fortinet, HPE Networking Instant On and Microsoft 365 with local support, and is an ASUS reseller; every order comes with a GST invoice, and the items above were in stock at the time of writing. Browse Fortinet FortiGate firewalls and HPE Networking Instant On, or see our corporate accounts page. Tell us your headcount and how staff work, and we will suggest a network layout and licence mix: call (65) 6978 3502 or email Sales@sourceit.com.sg.
Frequently asked questions
Is BYOD allowed under the PDPA? The PDPA does not ban it. Organisations must make reasonable security arrangements to protect personal data, and the PDPC's guide says protections for portable devices should apply to employee-owned devices too.
Is guest Wi-Fi enough for personal laptops? It keeps personal laptops off your internal network, which is the main network risk. It does not control company data opened in cloud apps, so pair it with app protection or device compliance rules.
Can we protect company email on a personal device without managing the whole device? Yes. Microsoft says Intune app protection policies work on devices not enrolled in any MDM and apply only to company data, including selective wipe.
Which Microsoft 365 plan includes Intune? Microsoft lists Intune Plan 1 as included in Microsoft 365 Business Premium; Business Basic and Business Standard do not include it.
Do we need a firewall if we already have guest Wi-Fi? A firewall enforces the rules between network segments and inspects traffic. A separate guest network is the first step; a firewall such as a FortiGate lets you control exactly what each segment can reach.
What about contractors who bring their own laptops? Give them guest Wi-Fi and access through a virtual desktop such as a Windows 365 Cloud PC, so company data stays off their device.